For compliance teams
Reduce manual administration and improve visibility.
Most compliance teams run on spreadsheets, shared drives and reminders someone set up years ago. GibComply replaces the tracker, not the team.
Compliance officers · MLROs · Compliance analysts
Audit log
Every create, edit and delete across the workspace
- Mon
Tom AshworthSigned
Quarterly return · 2026-Q2
Locked on signing
What you are accountable for
The questions you bring, and where GibComply answers them.
- Tracking obligations and deadlines
- Checkpoints and deadlines from the records you keep, with alerts to the owner.
- Ownership
- Regulated individuals with due-diligence status and attestations, and team roles for who can change what.
- Evidence
- Documents filed against the requirement they support, private to your workspace.
- Audit preparation
- A change log nobody can edit, CSV exports of every register, and their own login for auditors and lawyers.
In the product
The parts of GibComply you will use most.
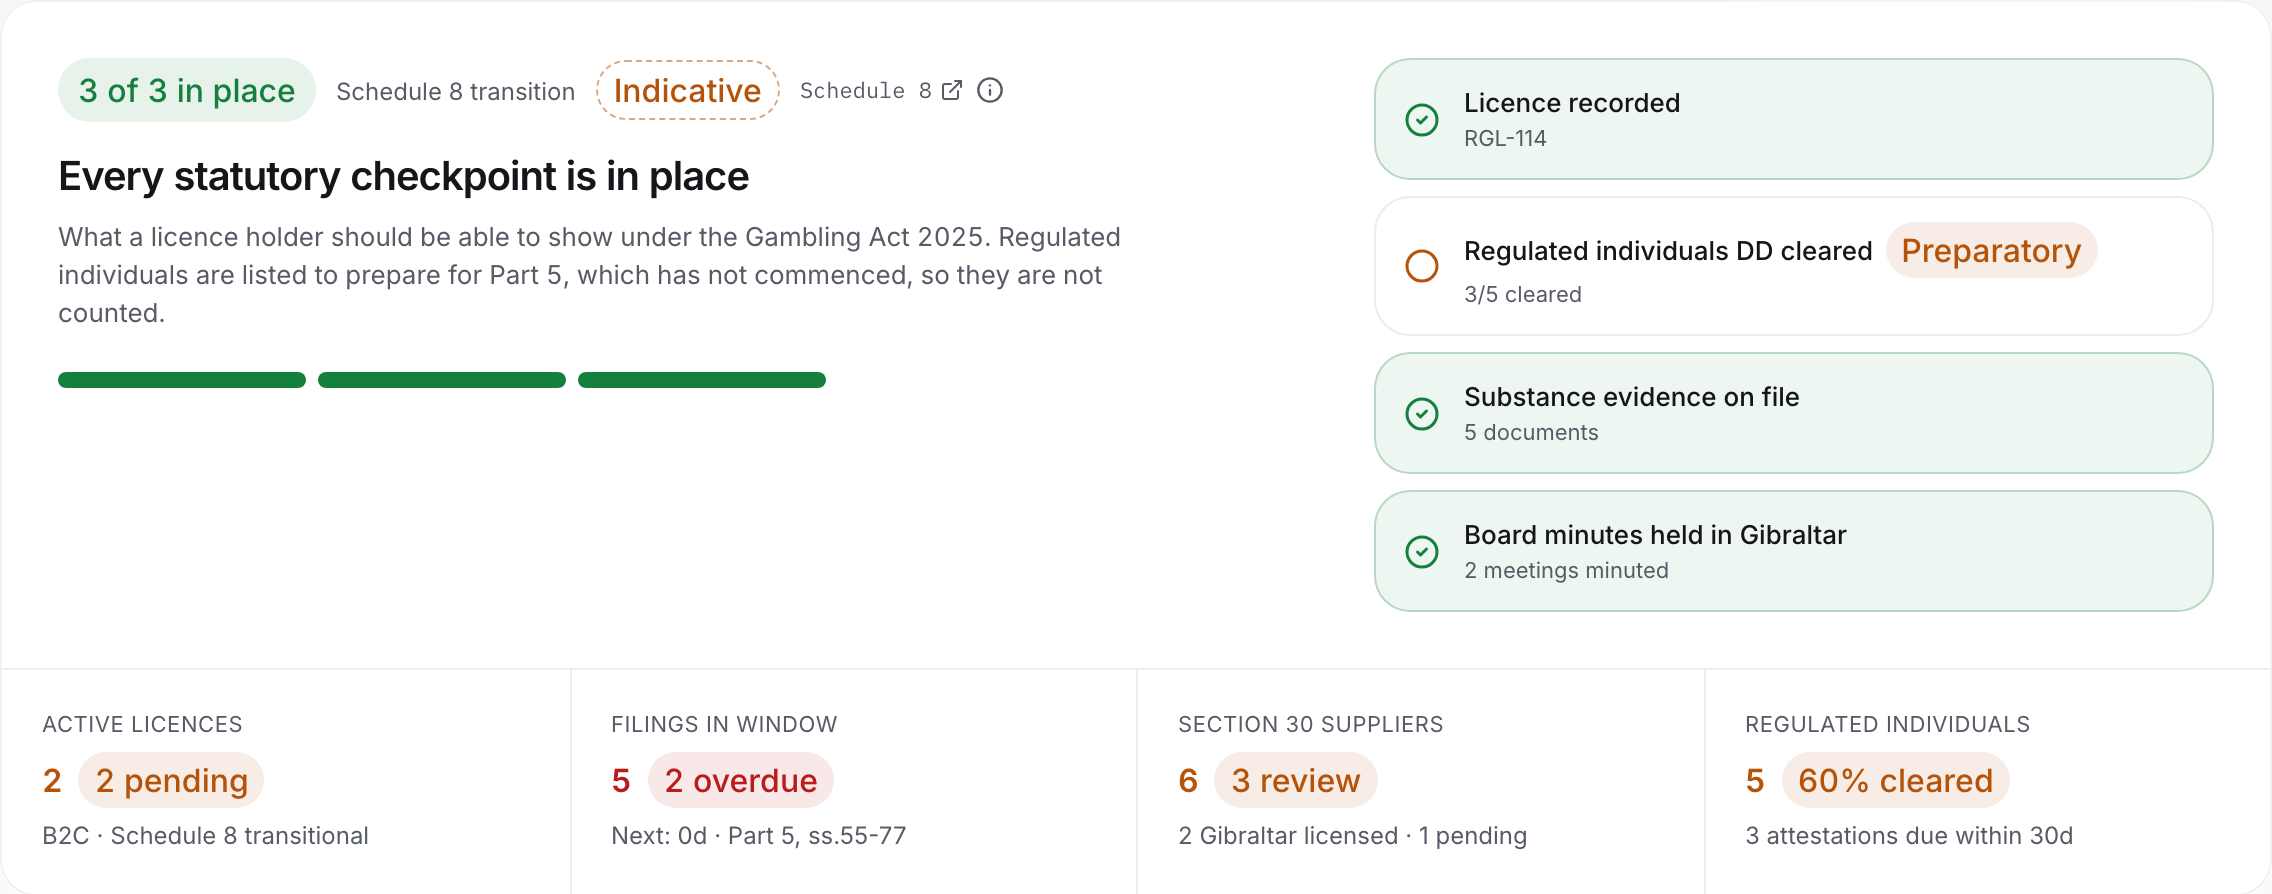
Obligations
See what is in place, what is outstanding and what is due, for every licence you hold.
- Statutory checkpoints from your own records
- Deadline alerts at 90, 60, 30 and 7 days
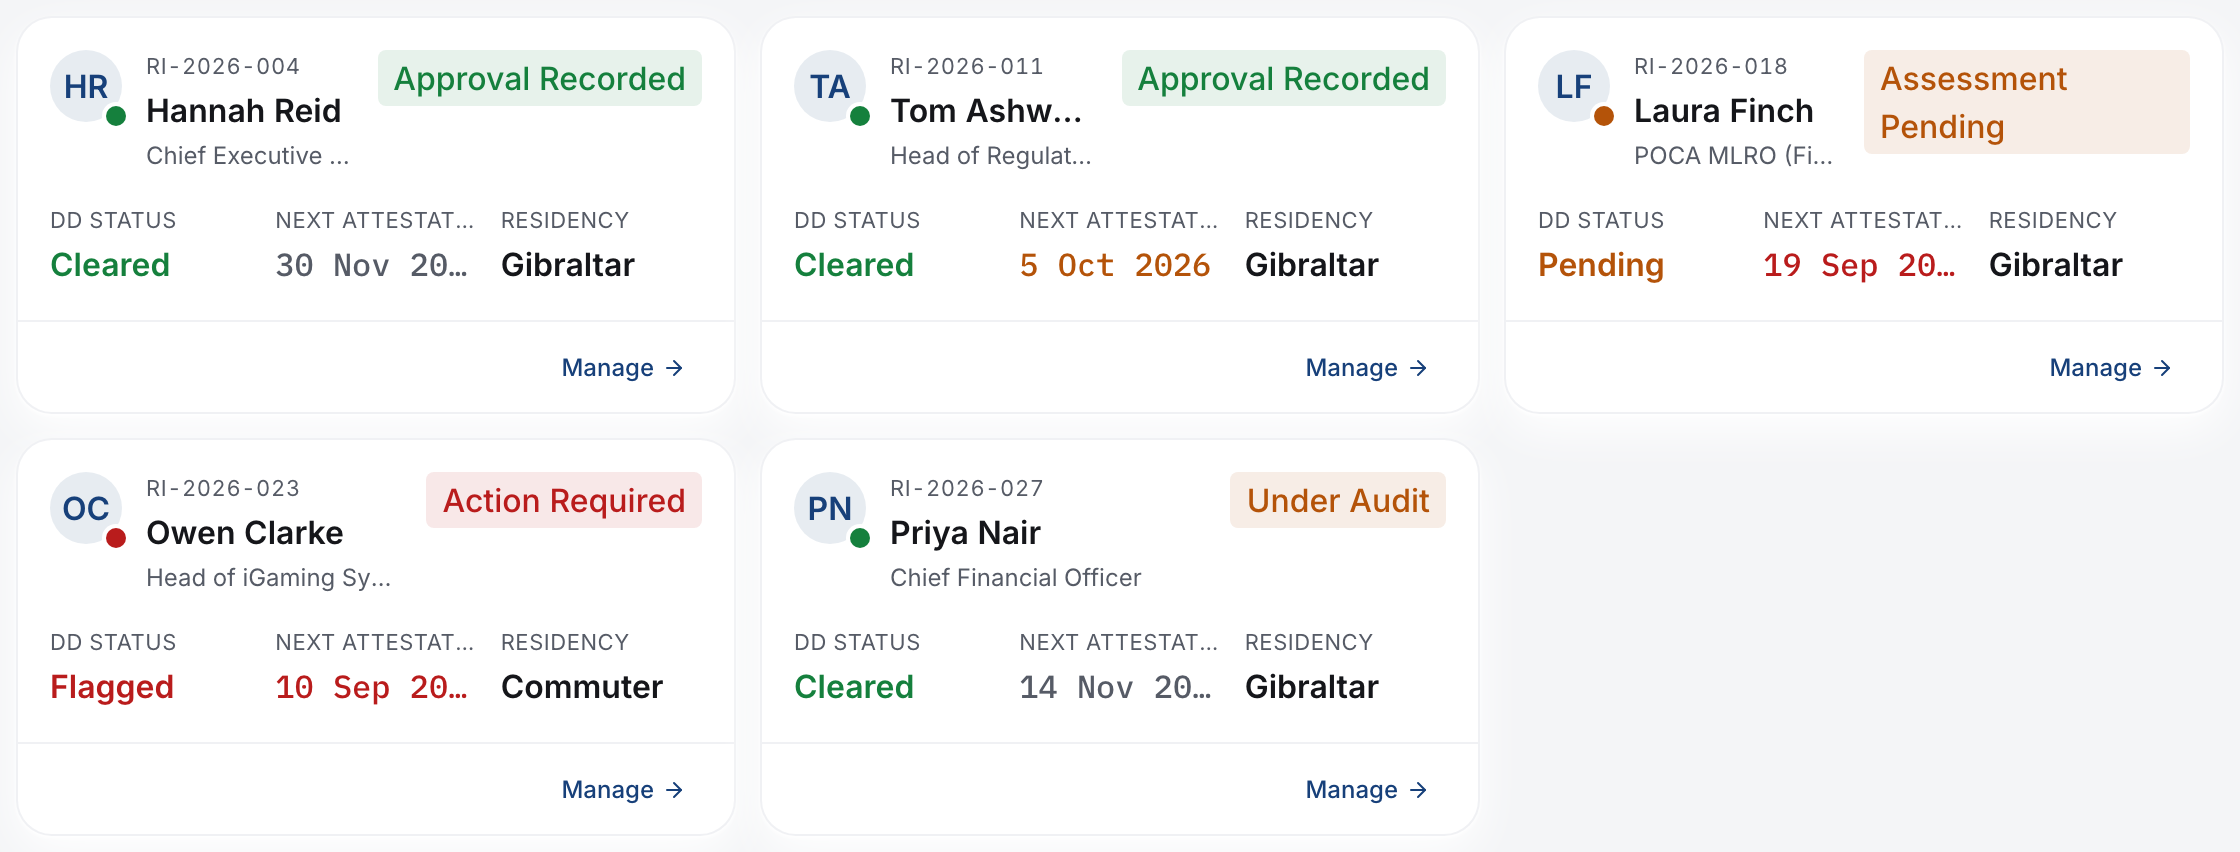
Individuals
Everyone in a regulated function on one register, with due diligence and attestations.
- Due-diligence status per person
- Quarterly attestations with the next due date
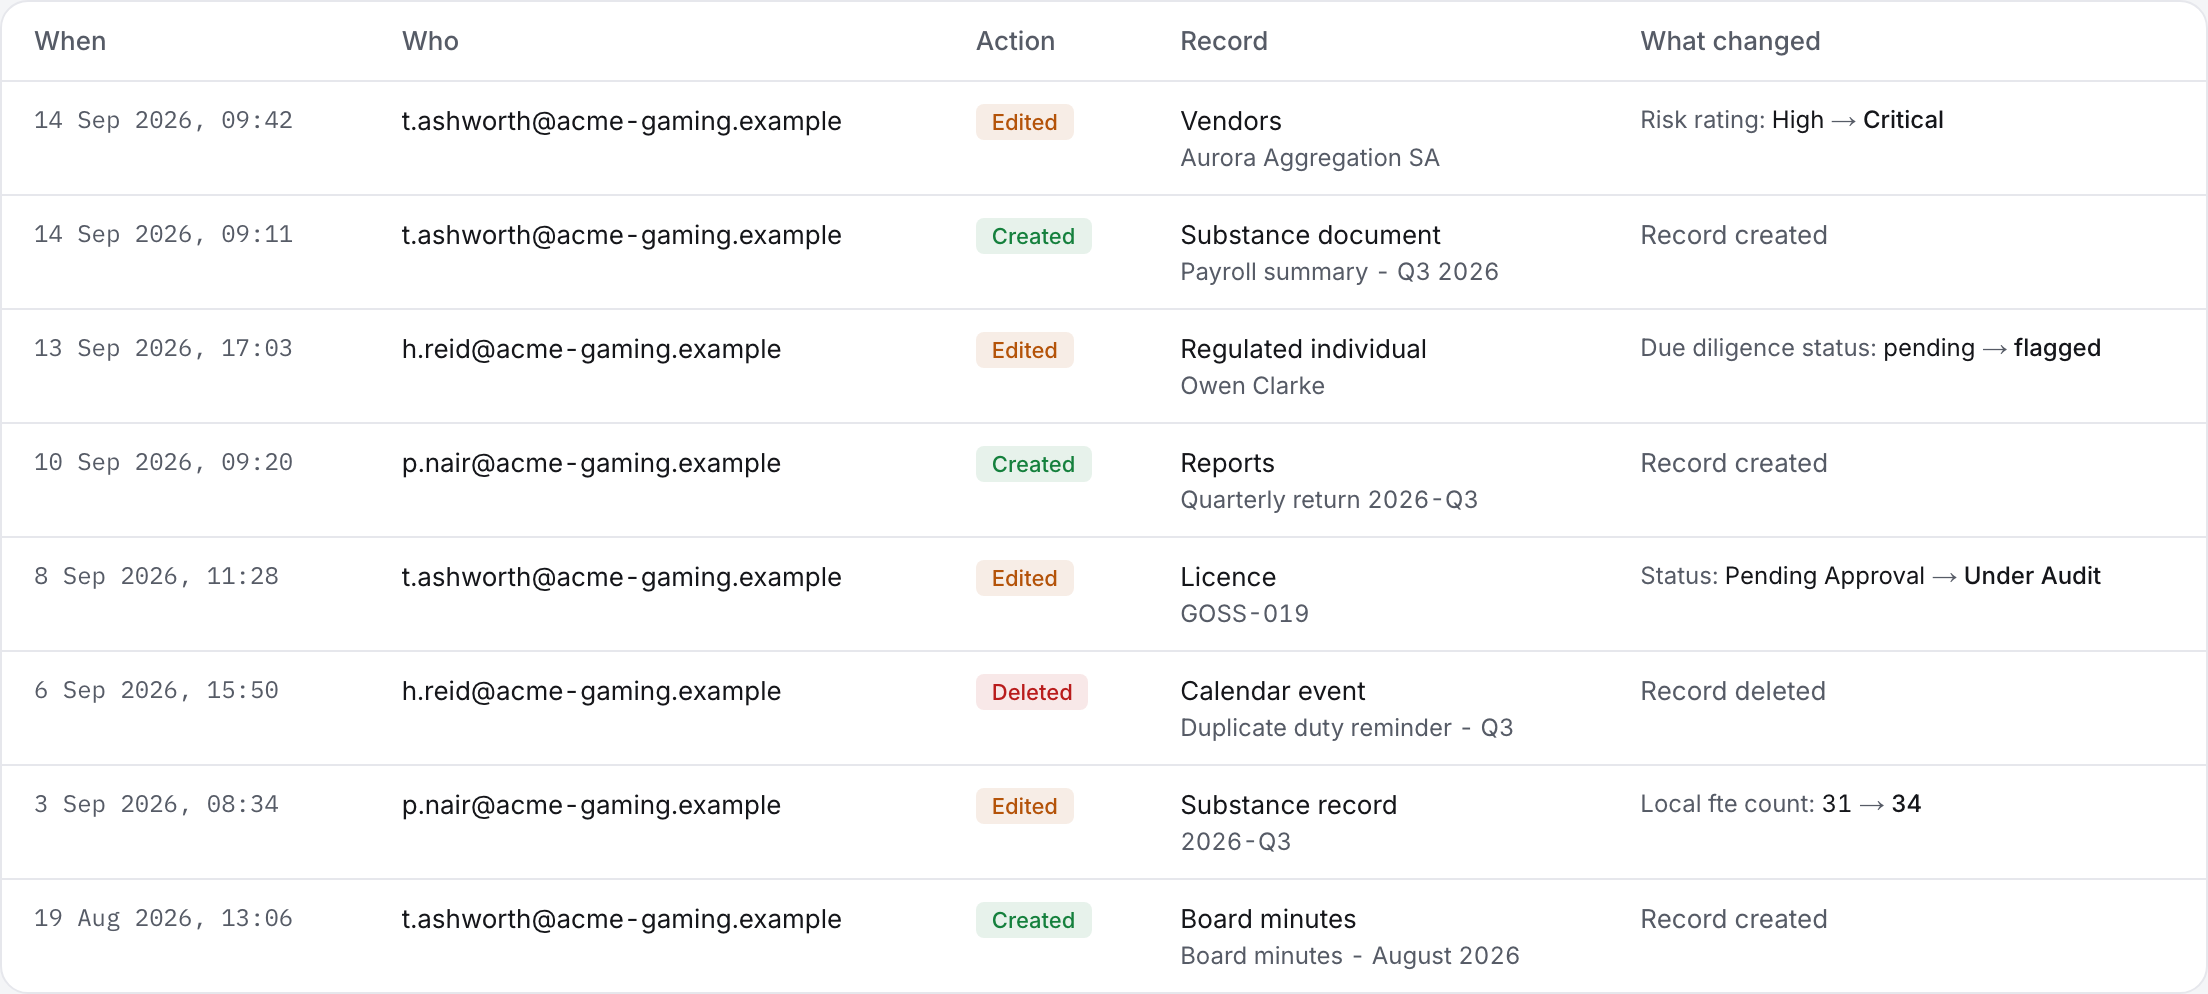
Change log
Every create, edit and delete across the workspace, with who did it and what changed.
- Cannot be edited or cleared, even by the owner
- Before and after values
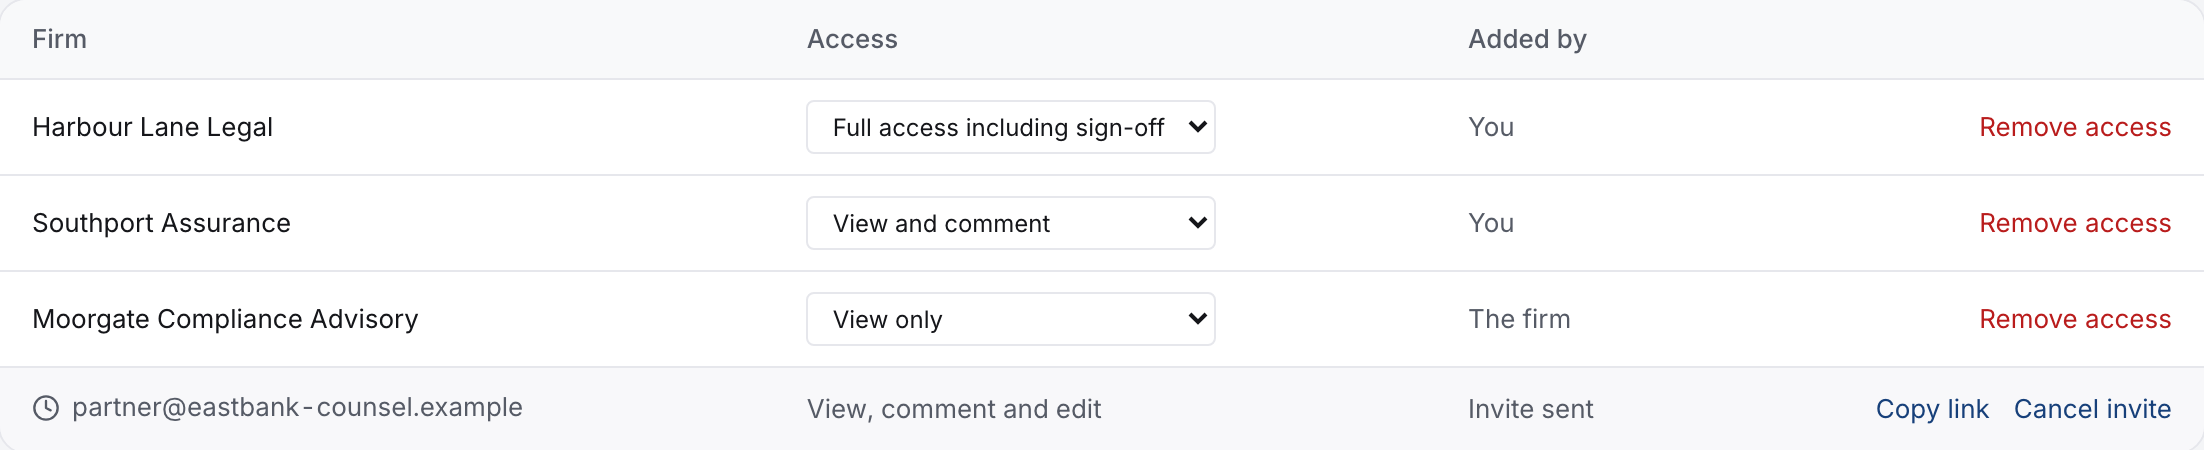
Auditor access
Give your lawyer, auditor or outside compliance officer their own login and a defined level of access.
- Four levels, from view only to sign-off
- They never see licences, suppliers, marketing or your team
Security
Controls built for regulated information.
Compliance records are evidence. Every control below is in place today.
Your data is yours alone
Each organisation's records are kept separate and can never be seen by another.
A record nobody can rewrite
Every change is logged with who made it and when. The log cannot be edited or cleared, even by an administrator.
Two-step sign-in
Authenticator-app codes for every user, and strong password rules by default.
Access by role
Owner, compliance officer and member roles, plus four access levels for outside advisers.
Encrypted throughout
Encrypted in transit and at rest. Connection credentials are encrypted before they are stored.
Private documents
Evidence files are private to your workspace and open only through expiring links.
Locked once signed
Signed returns, scope determinations and exported packs cannot be changed afterwards.
AI that never decides
Where AI helps, it is labelled, every answer is sourced, and a person keeps the final say.
Bring your Gibraltar compliance into one system.
Obligations, evidence, responsibilities and reporting under the Gambling Act 2025, in a workspace your compliance officer, your board and your auditors can rely on.